Skip to content

The Cost of Delayed Breach Detection and the Value of Proactive Security Monitoring
Detecting a cyber intrusion quickly is one of the most important parts of cybersecurity. Once an attacker gains access to your network, every minute matters. The sooner you identify the breach, the better your chances of limiting damage, protecting sensitive data, and restoring normal operations.
The Hidden Threat: Undetected Intrusions
Cybercriminals rarely kick the door down. Instead, they slip in quietly, through phishing emails, unpatched software vulnerabilities, or cleverly disguised malware. Once inside, they often move laterally across systems, gathering sensitive data or preparing larger attacks like ransomware deployment.
What makes this especially dangerous is that attackers can remain undetected for weeks or even months. During that time, they may be extracting valuable information, compromising systems, or positioning themselves for maximum disruption. The longer they stay hidden, the more damage they can cause.
Why Detection Time Varies
There’s no universal timeline for identifying a breach. Some organizations, like 46Solutions, catch suspicious activity within hours thanks to strong monitoring systems and well-trained teams. Others may not realize they’ve been compromised until long after the damage is done.
Several factors influence detection time, including:
- The strength and sophistication of cybersecurity tools in place
- The consistency of network monitoring and threat analysis
- The skill level and persistence of the attacker
Organizations with proactive defenses and real-time alerts are far more likely to detect and respond quickly.
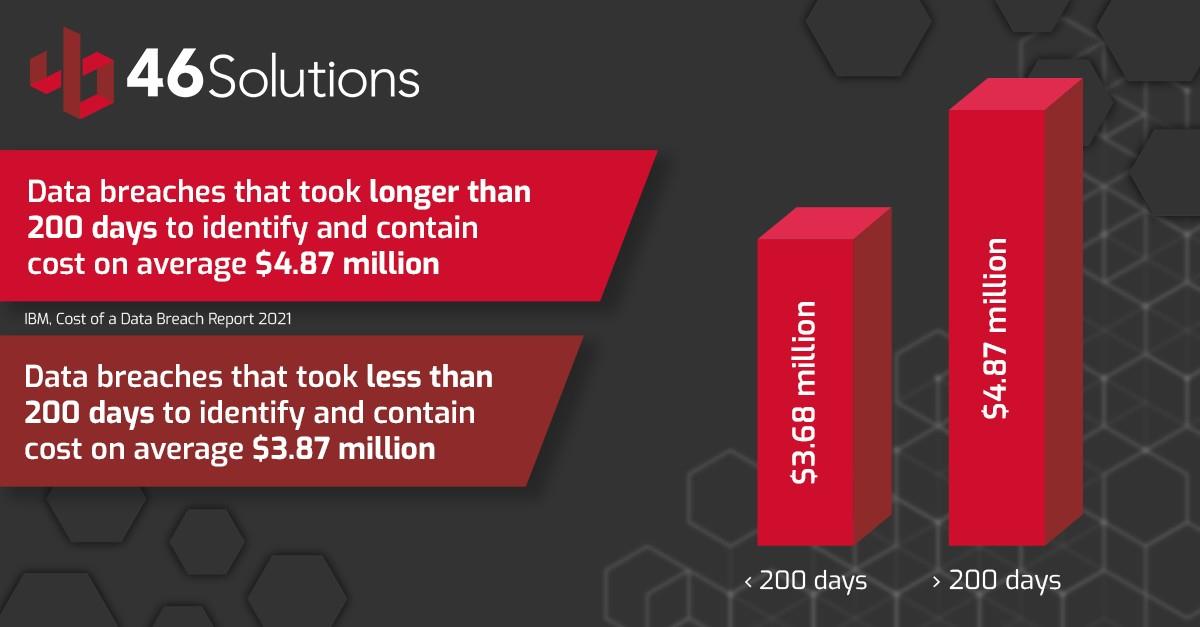
The High Cost of Delay
Delayed detection can be incredibly expensive, not just financially, but reputationally. While attackers operate within a compromised network, they may:
- Steal sensitive customer or business data
- Disrupt operations or shut down systems
- Deploy ransomware and demand payment
The longer they have access, the more complex and costly the recovery becomes. What could have been a contained incident can escalate into widespread system failure, regulatory penalties, legal challenges, and a loss of customer trust.
Recovery: More Than Just Fixing the Problem
When a breach goes undetected for an extended period, recovery isn’t as simple as removing malware. Organizations may need to:
- Conduct a full forensic investigation
- Rebuild parts, or all, if their network infrastructure
- Notify affected customers or stakeholders
- Address legal and compliance obligations
These steps can take weeks or months and often come with high costs.
The Case for Proactive Monitoring
The best defense against prolonged breaches is proactive monitoring. Organizations like 46Solutions, that continuously track network activity and respond to anomalies in real time dramatically reduce detection time, and, in turn, minimize damage.
This is where experienced cybersecurity partners can make a meaningful difference. With the right tools and expertise, businesses can stay ahead of threats instead of reacting after the fact.
A Smarter Approach to Cybersecurity
A member of the Elliot Family of Brands, 46Solutions, a locally operated, employee-owned company based in Lexington, focuses on helping organizations take a proactive stance. With over 350 years of combined technical experience, their team specializes in continuous monitoring and rapid threat response.
By identifying suspicious activity early and acting quickly, they help businesses limit exposure, reduce recovery costs, and maintain operational stability.
Peace of Mind in an Uncertain Landscape
Cyber threats aren’t going away—but the risks they pose can be managed. Faster detection leads to faster response, and that can make all the difference.
Investing in proactive cybersecurity isn’t just about protection; it’s about resilience. When your systems are actively monitored and your defenses are always on, you’re not just reducing risk, you’re taking control of it.